
Turn abandoned patents
into your own filing
into your own filing
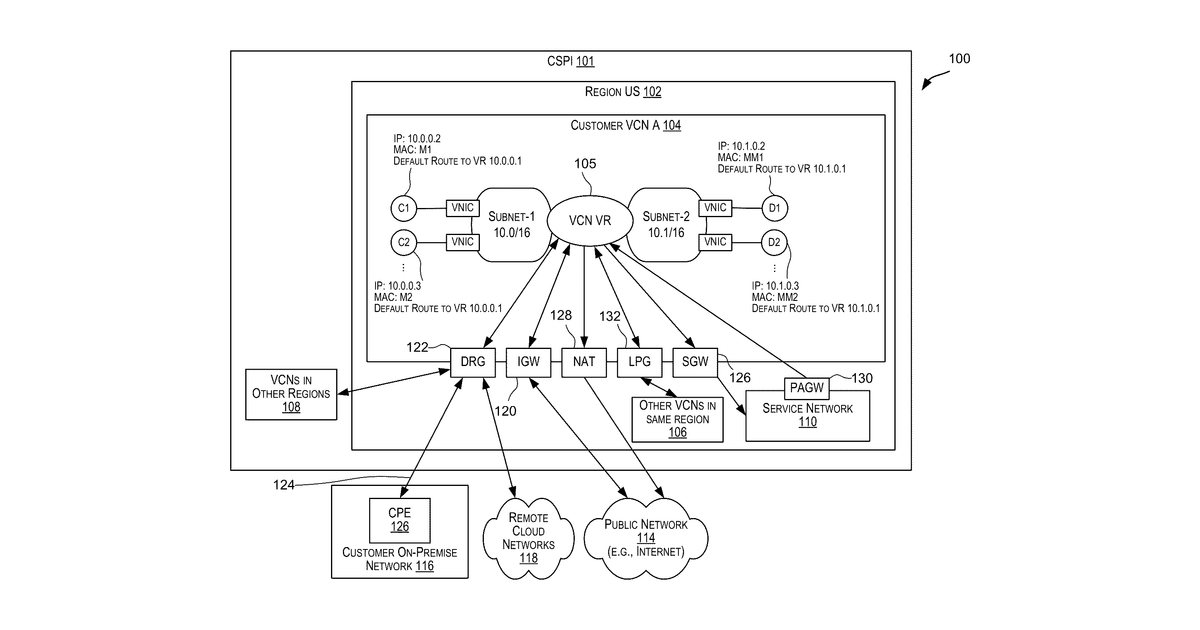
This invention describes a system for protecting sensitive data by tagging it with "taints" and then enforcing rules about where that tainted data can go within a network. Instead of just blocking access at the network edge, specific rules (called assertions) are set up to control data movement at various points inside the network. For example, a rule might say "Red data never leaves my company's cloud space." The claims specifically detail a method where data is tagged, rules are accessed, and these rules are enforced by different network points, which can also communicate and share these data tags.
Why it matters: The rapid expansion of multi-cloud and hybrid environments since 2024 has further eroded traditional network perimeters, making data-centric security approaches like this more critical. Advances in data classification and policy orchestration tools also make implementing such a system more feasible.
AI gives you a few directions you could take this. Pick one, and we check whether your version is different enough to patent, then write the filing.
Reinvent this with AI


